Passive mapping and risk analysisfor industrial networks

The UMX Explorer passive probe inventories the industrial network without sending anything onto it. UMX Risk Manager turns it into an IEC 62443 risk analysis and a costed action plan.

UMX ExplorerNetworksPassive listening
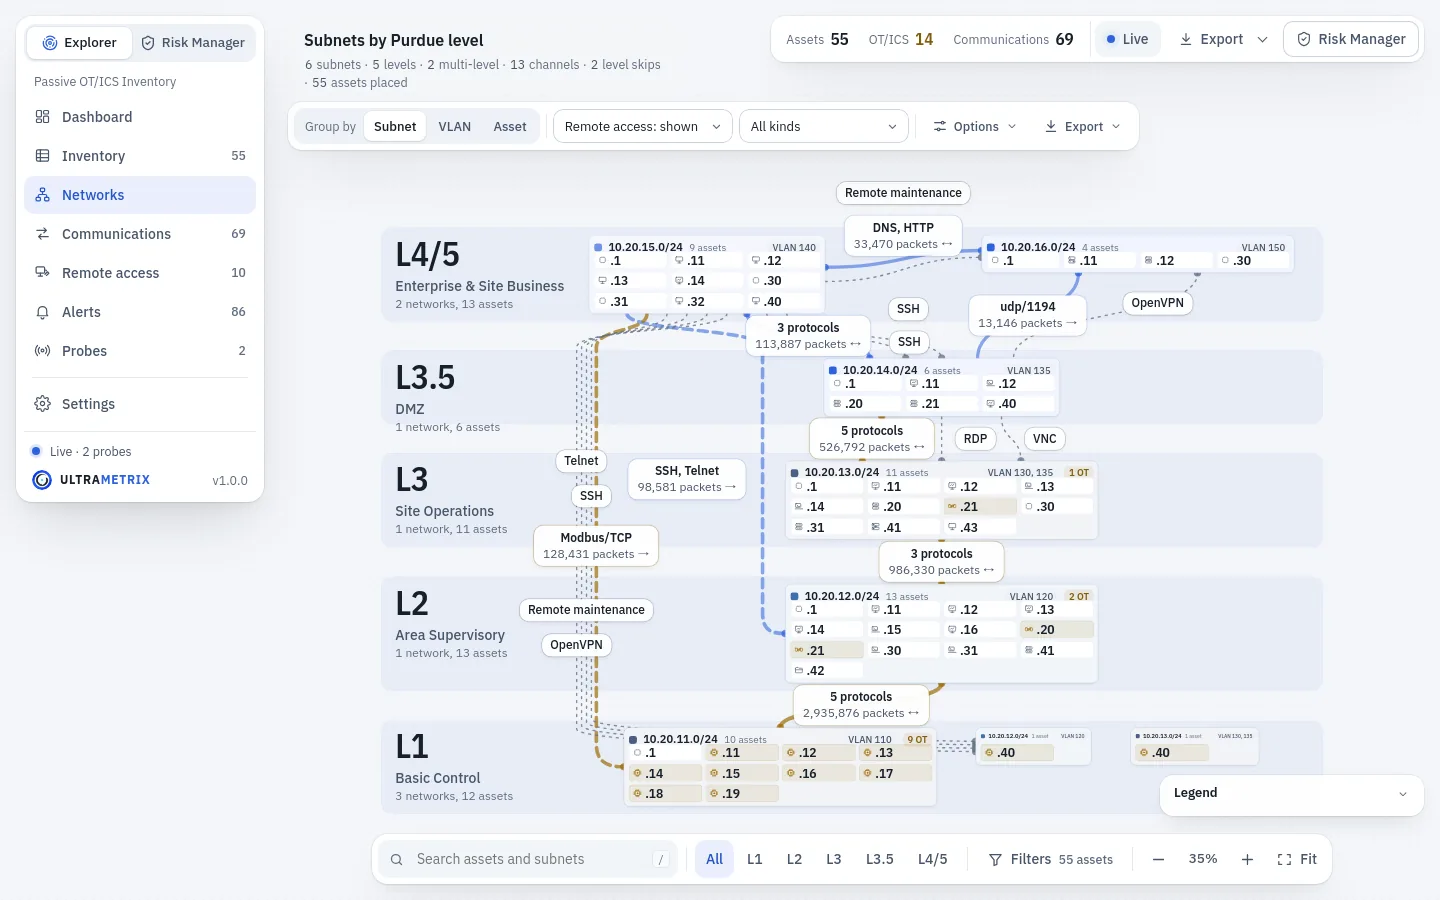
UMX Explorer, Networks view: 55 assets placed on five Purdue levels, from L1 Basic control to L4/5 Enterprise, with the channels observed between subnets.
Capture of UMX Explorer on Ultrametrix's demonstration plant. The animation follows the channels the capture shows and adds no data to it.

From the mirror port
to the decision page

The process has four steps. Every image is a capture of the consoles, taken on Ultrametrix's demonstration data.

Connect

The probe plugs into a mirror port. Nothing is installed on the controllers.

A copy of the traffic

The switch copies the traffic to the probe through a mirror port (SPAN) or a TAP. The probe listens without sending anything: over a 24-hour bench test, no frame left its capture port.

Every mirror port checked

The console shows the traffic received port by port. The umx doctor command checks that the mirror session carries exchanges between other machines.
Observe

The inventory is built from the exchanges observed on the network.

Controllers identified by their protocols

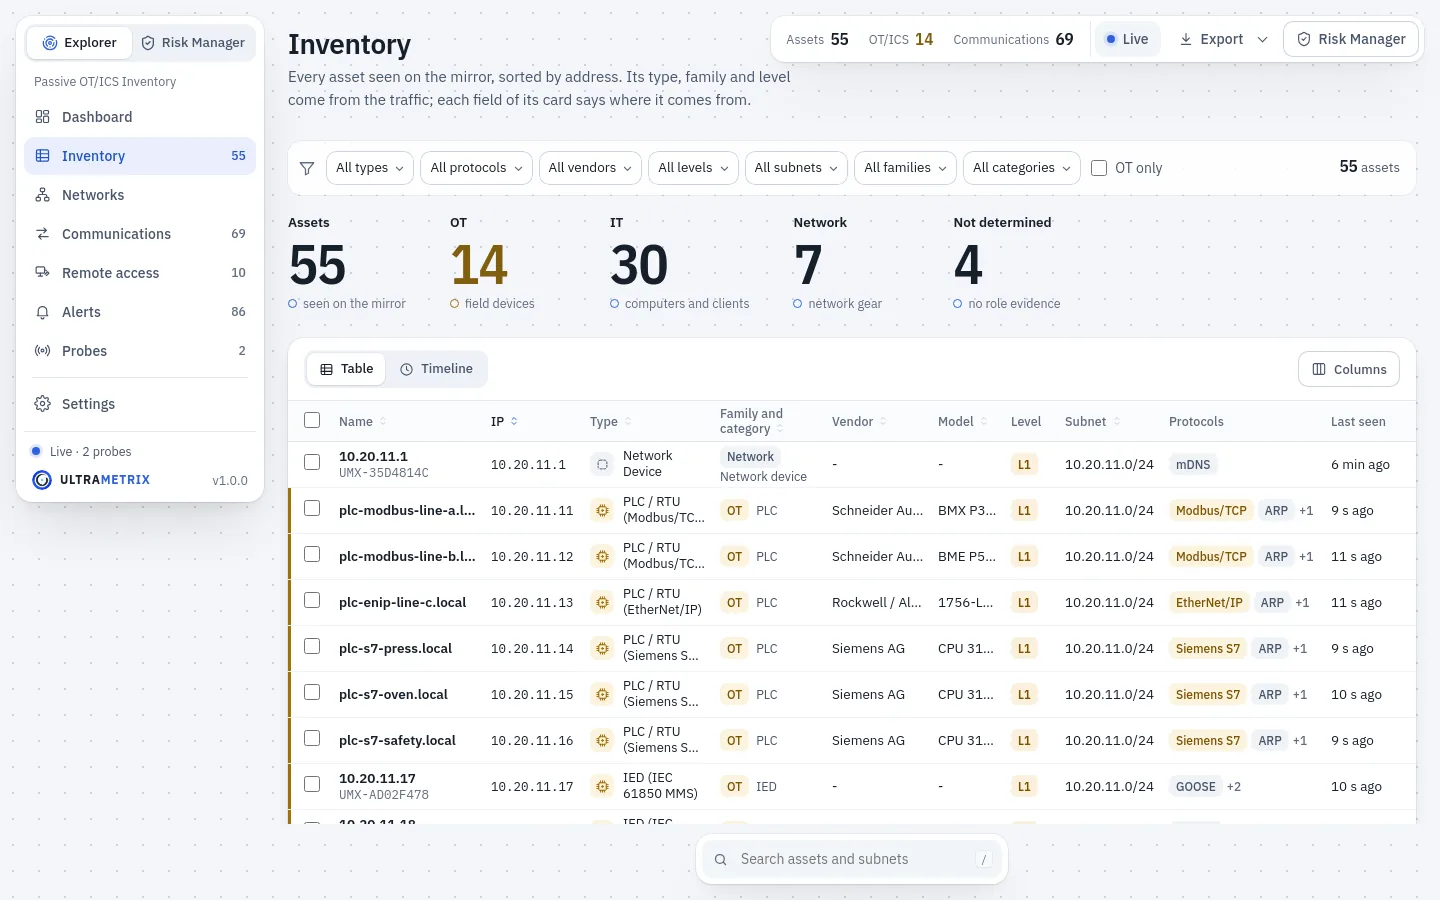
Vendor, model and firmware version are read in the Modbus, S7 or EtherNet/IP answers. Every field gives its source; a value not seen is marked “not observed”.

Purdue levels and flows between networks

Each asset is placed from the structure of its exchanges, never from an address range. The flows between subnets are drawn and counted.

Remote access

For SSH, Telnet, VNC, RDP, SMB and VPNs: who connects to which device, when, and whether the channel is encrypted. It is read in the protocol, not inferred from the port number.

Analyze

UMX Risk Manager builds the IEC 62443 risk analysis from that map.

Zones and conduits, proposed then validated

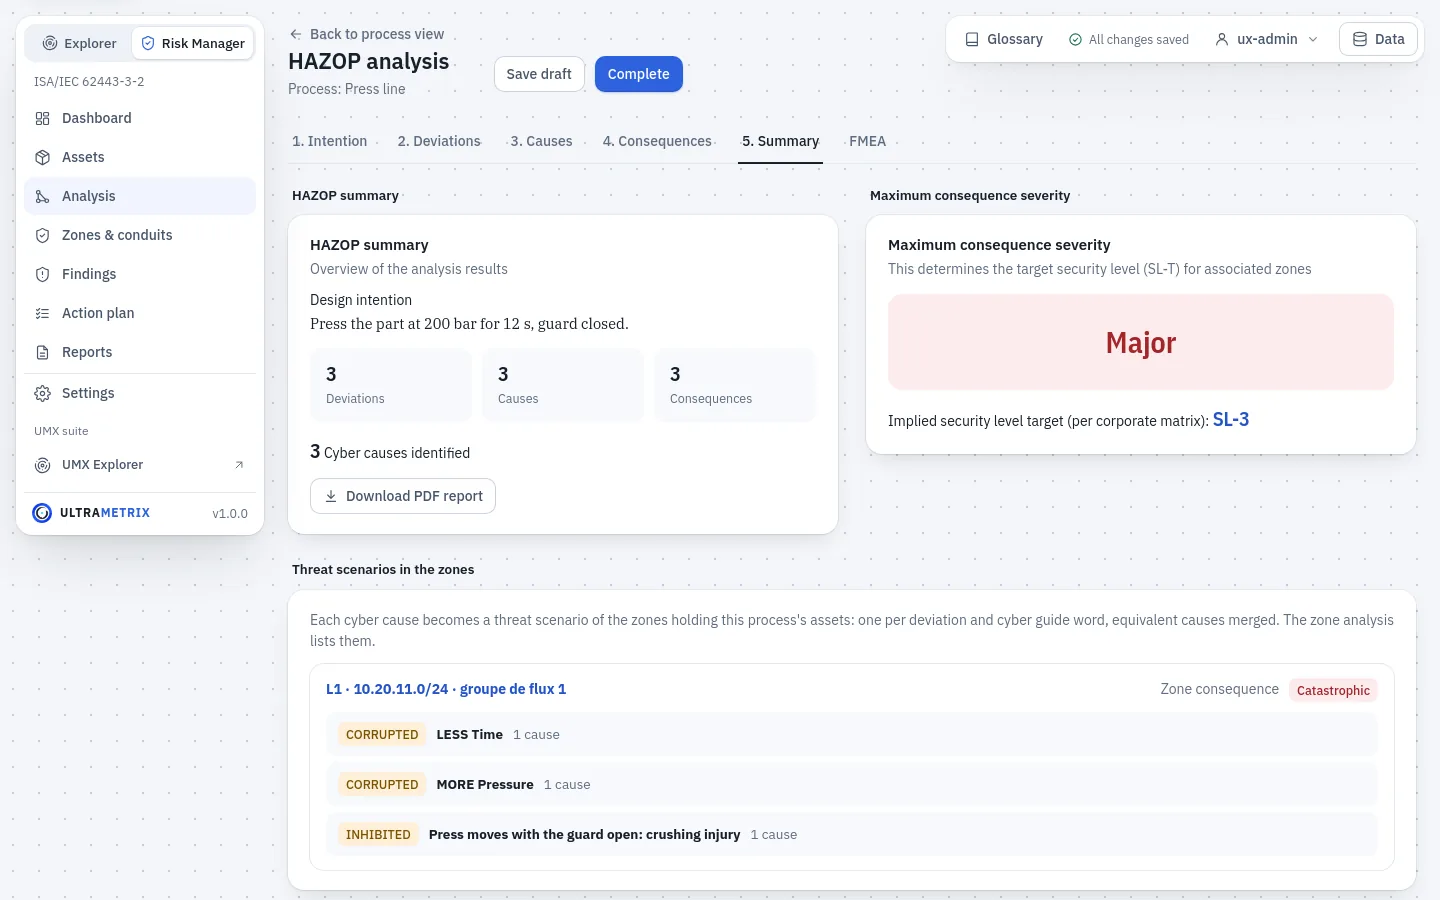
Risk Manager proposes zones from the capture. Your engineer confirms, renames or splits them. The HAZOP study then sets the target security level (SL-T).

Risk before and after countermeasures

Inherent risk, analyzed risk, then current and planned residual risk. Every score shows its calculation and the share of the evidence that is inferred or potential.

Costed action plan

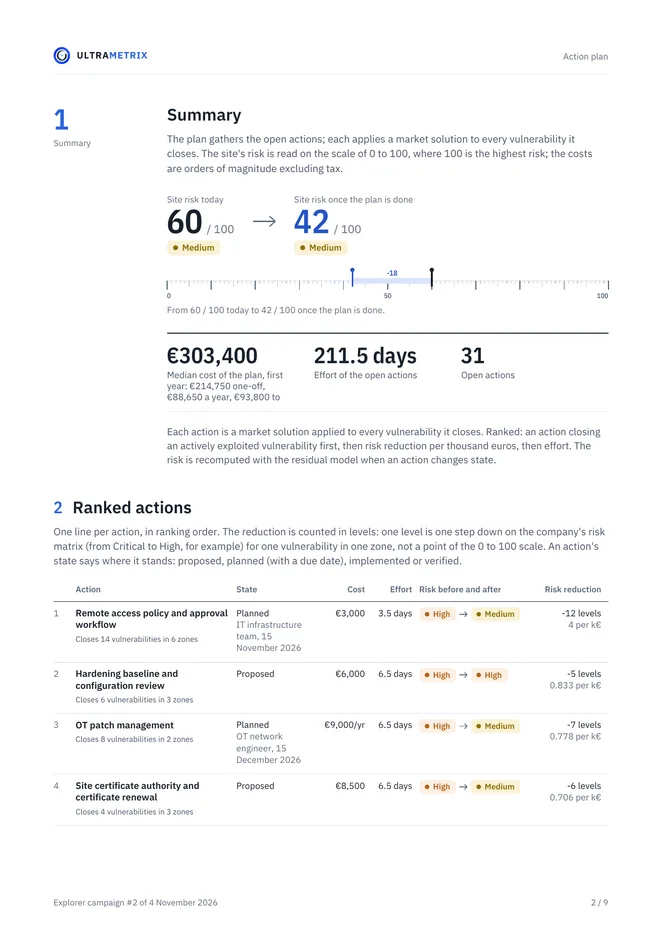
Every countermeasure carries a cost, an effort and the risk it removes per thousand euros. The actions are ranked by that ratio.

Decision page

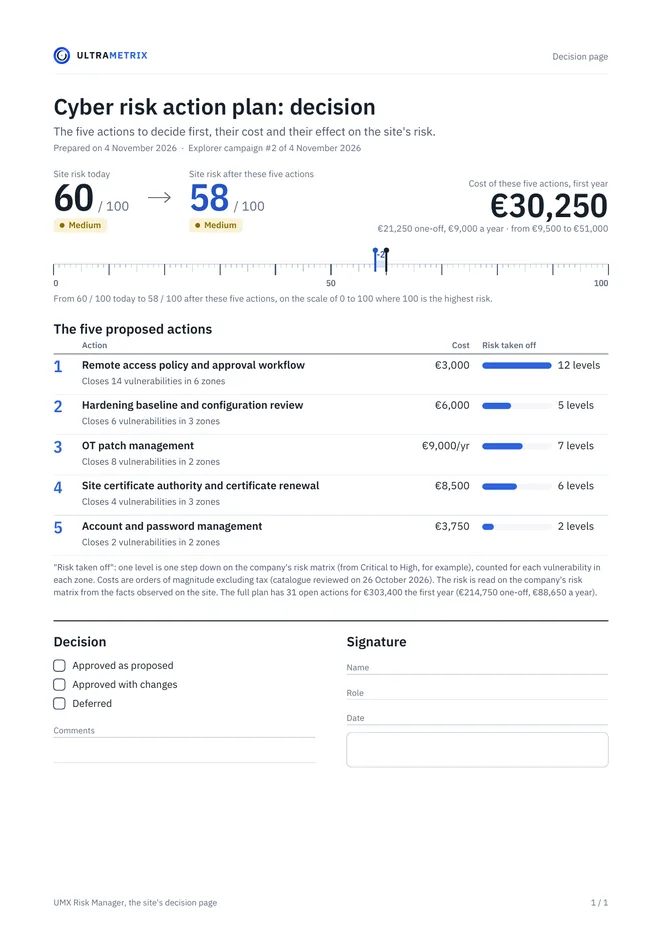
The first five actions, their cost and the risk each one removes, with a decision and signature block for management.

Document

From the analysis, Risk Manager produces the reports and the projection onto the ReCyF.

Projection onto the ReCyF

The analysis is projected onto the 20 objectives of ANSSI's ReCyF v2.5, a working document. Every status points to the project's dated evidence or to the declaration to provide. The projection helps prepare the NIS2 file; it is neither a certificate nor a compliance verdict.

Seven reports

Risk analysis of the site and of each zone, decision page, ReCyF audit, action plan, registers of remote access and of risk acceptances.

UMX ExplorerMirror portDiagram

Computed by UMX Risk Manager

Results on the demonstration plant

Figures produced by the consoles on the demonstration plant, an industrial network simulated by Ultrametrix with emulated controllers. None comes from a customer site; all can be reviewed in a demonstration.

Decision page

€30,250

for the first five actions

Ranked by risk removed per euro, with their cost and the vulnerabilities they close.

  1. 1Remote access policy and approval workflow14 vulnerabilities
  2. 2Hardening baseline and configuration review6 vulnerabilities
  3. 3OT patch management8 vulnerabilities
  4. 4Site certificate authority4 vulnerabilities
  5. 5Account and password management2 vulnerabilities

Costs as orders of magnitude excluding tax, €9,500 to €51,000 for the five.

55 assets, including 14 OT

The demonstration plant as the probe saw it, then imported into Risk Manager. One square stands for one asset.

16

security zones proposed from the capture

Five of them were still to be confirmed by an engineer on the day of the capture.

37

costed actions in the plan

Each with its cost, its effort and the risk it removes.

26

passive findings to handle

Including four skipped Purdue levels and an OT-to-IT flow, read in the traffic, without an active scan.

20

ReCyF v2.5 objectives projected

Each status linked to dated evidence or to the declaration to provide, to prepare the NIS2 file.

Protocols decoded

Industrial

  • Modbus/TCP
  • S7comm
  • EtherNet/IP (CIP)
  • DNP3
  • IEC 60870-5-104
  • IEC 61850 MMS, GOOSE
  • BACnet/IP
  • PROFINET DCP
  • EtherCAT
  • CC-Link IE
  • OPC UA
  • MQTT
  • HART-IP
  • KNX

Remote access

  • SSH
  • Telnet
  • VNC
  • RDP
  • SMB
  • IPsec
  • OpenVPN
  • WireGuard

Two modules
linked by an export

UMX Explorer

Free, 100% passive

A factual inventory, with no risk interpretation

  • Passive inventory: controllers, HMIs, workstations, servers
  • The Purdue level of every asset and the flows between networks
  • Remote access, with its encryption
  • Probes as a fleet, a PCAP file or a single capture
UMX Explorer inventory: Schneider, Rockwell and Siemens controllers with their model and level.

UMX Risk Manager

IEC 62443-3-2 risk analysis

Risk analysis and action priorities

  • Zones and conduits, HAZOP, target security levels
  • Inherent, analyzed and residual risk
  • Costed action plan, decision page
  • Projection onto the ReCyF v2.5, seven reports in French and English
HAZOP summary in Risk Manager: the most severe consequence sets a target security level SL-3.

Threat intelligence module (CTI)

Off by default. Once on, it sends only the scope the operator confirms: domains, public addresses, brands, keywords and products (vendor, model, version). The inventory, the topology and the risk analysis do not leave the site.

Reports produced by Risk Manager

Seven reports, in French and in English, produced from the console for management and auditors.

Decision page
Decision pageFor management
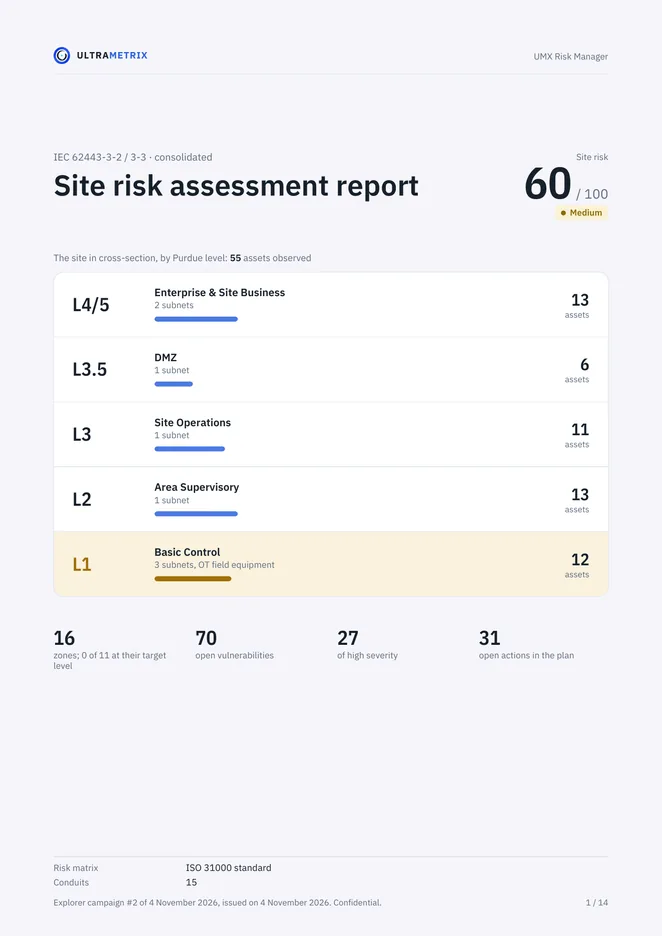
Site risk-analysis report, cover
Site risk analysisIEC 62443-3-2
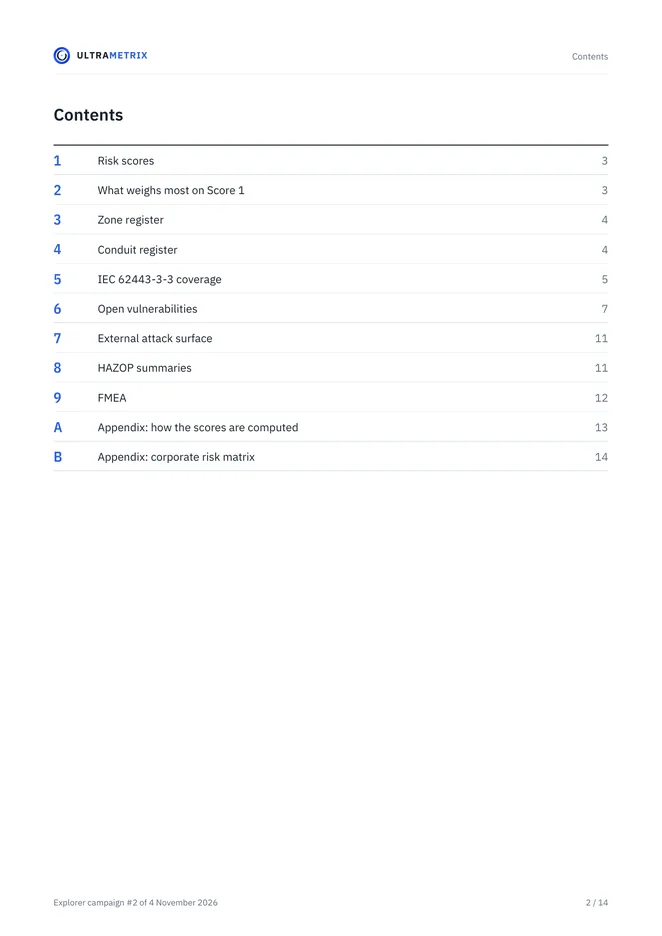
Site risk-analysis report, contents
Risk analysis, contentsZones, conduits, HAZOP
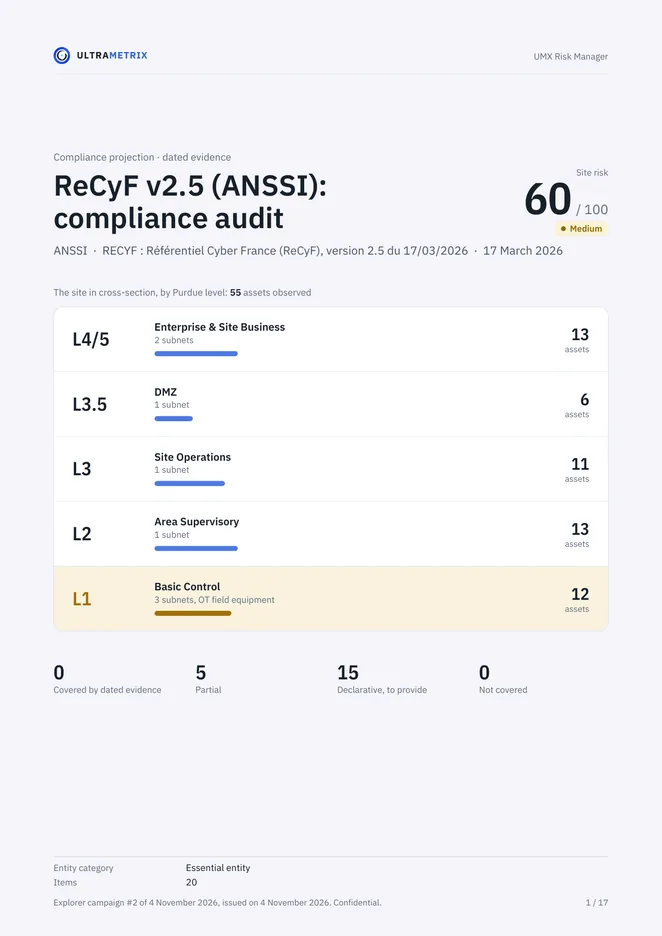
ReCyF v2.5 compliance audit, cover
ReCyF v2.5 auditNIS2 preparation
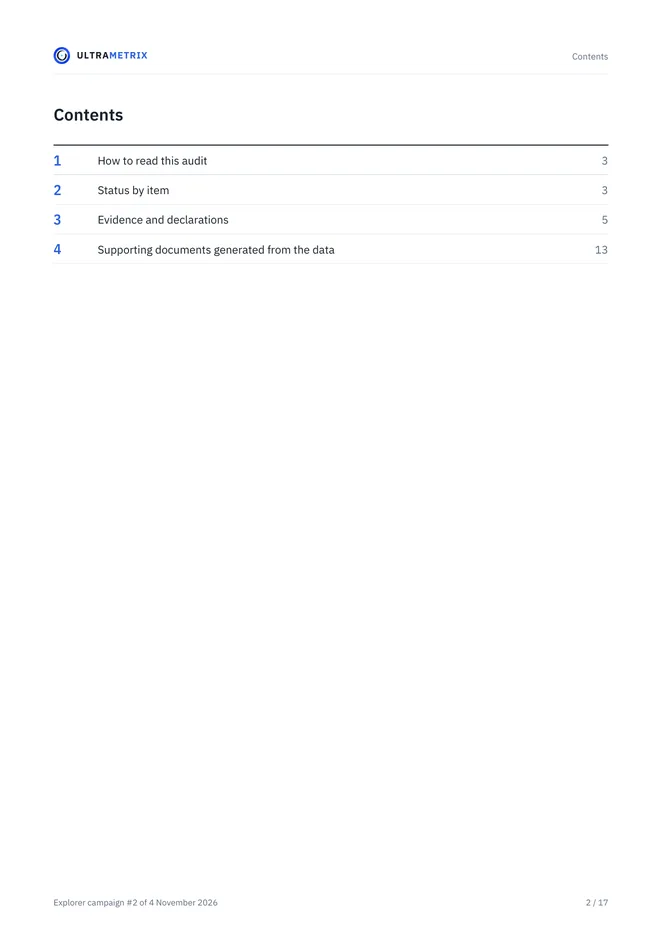
ReCyF v2.5 compliance audit, contents
ReCyF audit, contentsEvidence and declarations
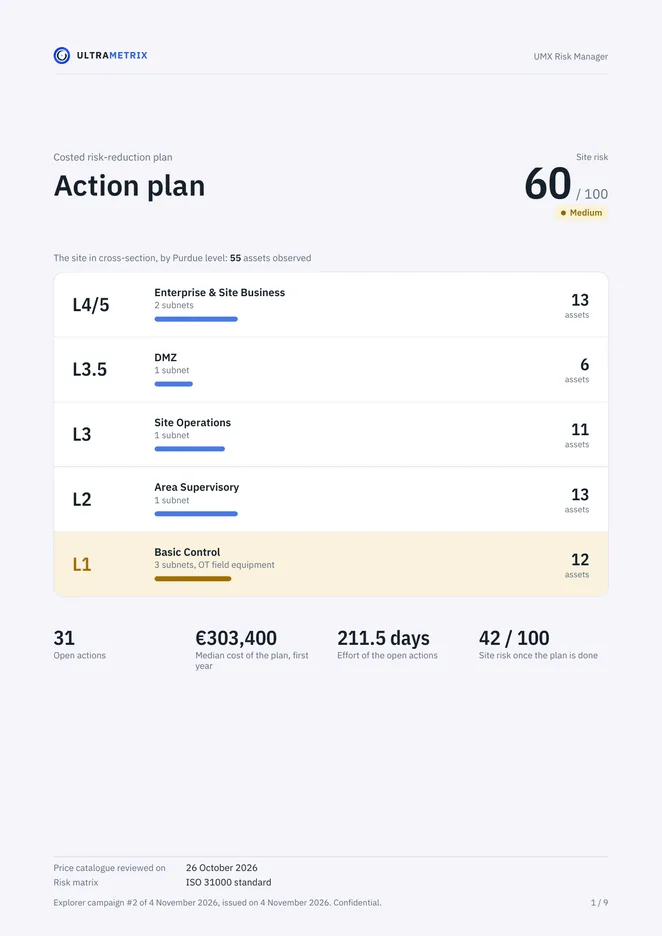
Action plan, cover
Action planRisk removed per euro
Action plan, ranked actions
Ranked actionsCost, effort, effect
  • Also in Risk Manager
  • Report per zone
  • Register of remote access
  • Register of risk acceptances
  • CSV exports

Runs on site, offline by default

The probes, the central console and Risk Manager run inside your network, including an isolated one. Two functions can reach the outside, both off by default: the CTI module, limited to the scope the operator confirms, and the check for new versions.

Your siteeven without an outside connectionProbe L1-L2mirror portProbe L3-L4mirror portCentral consolehub and UMX ExplorerRisk Manageranalysis, plan, reportsNever leave:inventory, topology, riskCTIoff by defaultsends only whatthe operator confirmsOutside
Your siteeven without an outside connectionProbe L1-L2mirror portProbe L3-L4mirror portCentral consolehub and UMX ExplorerRisk Manageranalysis, plan, reportsNever leave:inventory, topology, riskCTIoff by defaultonly whatthe operator confirmsOutside

Ultrametrix

Non-destructive testing
and industrial cybersecurity

Ultrametrix is a non-destructive testing laboratory based in Saint-Genis-Laval, near Lyon, France. It examines parts and structures without altering them, for industry and buildings. UMX applies the same principle to the industrial network: observe without interfering.

Try it first

UMX Explorer is free: plug it into a mirror port and see what it finds on your network. The results shown here come from Ultrametrix's demonstration plant; with UMX, Ultrametrix opens a new activity.

Non-destructive testingIndustrial networkExamining the partwithout altering itReading the trafficwithout sending

Annual license per deployment

Indicative catalog prices, per year and per deployment.

UMX Explorer

Free

The passive inventory of the industrial network: free, no license to activate.

  • Passive probe, hub and console
  • Use with no time limit and on any number of networks
  • Download once you have a free account
Download

UMX Risk Manager

€4,500/year

The IEC 62443 risk-analysis console, fed by Explorer.

  • Explorer import, IEC 62443 zones and conduits
  • Three risk levels, action plan, reports
  • NIS2 audit (projection onto the ReCyF)
  • Annual license, updates and support included
Request a demo

UMX Risk Manager + CTI

€7,900/year

Risk Manager with threat intelligence: external sources, matched to the inventory.

  • Everything in Risk Manager
  • Threat intelligence: external sources, matched to the inventory, external exposure
  • CTI scans included in the price, capped each month per license
Request a demo

UMX Enterprise Suite

On quote

Several deployments, with dedicated support.

  • Several deployments
  • Dedicated support and deployment assistance
  • Integration options
  • Contract and invoicing offline, licenses issued by Ultrametrix
Ask for a quote

Full risk audit and support

Ultrametrix carries out or co-produces the risk analysis with your teams, from mapping to the final report, then makes you autonomous. On quote.

Contact Ultrametrix

Ultrametrix presents both products on the demonstration data. A trial of UMX Explorer on one of your mirror ports can follow.

You can also write to contact@ultrametrix.fr

For example: food plant, two lines, Siemens controllers.